Getting Started with DeskDirector
DeskDirector Portals
Browser Support
What is the DeskDirector Admin Portal?
What is the DeskDirector Tech Portal
What is the DeskDirector Client Portal?
Desktop Portal
Managing Your Account
Admin Essentials
DeskDirector Features Overview
Logging in to DeskDirector
User Profiles & Profile Pictures
Managing Tickets with DeskDirector
Office Hours
Getting Started with the Solution Library
How Searching Works
Embedding Help Page Media
Get started with the DeskDirector Power Automate Connector
Features
Portal Customization
Forms
Service Catalogue
Communication
Email Connectors
Notifications
Email Notifications
Actionable Messages for Emails
Real-Time Chats
Email Template Engine
Surveys
Broadcasts
Generative AI
DeskDirector with Generative AI
Ticket Summary for TECH Portal
Setting up AI Service Providers
Microsoft Foundry for DeskDirector
Knowledge Bases for AI Assistants
Custom Tools for AI Assistants
AI Assistants in DeskDirector
Advanced
Login & Authentication
Contact Groups
Custom Domains
File Storage
Dashboard
Accounts
Contacts
Approvals
Tags
Task Lists
The Learning Center
Portal Deep Linking
Auditing & Analytics
Microsoft Power Automate
Actions
Solutions
Featured Solution: Teams Ticket Discussion
Power Automate Template Gallery
Featured Solution: Ticket Briefing
Power Automate Administration
DeskDirector Power Platform Connector Reference
Power Automate Connector - Setting up your first flow
Microsoft Teams App
Introducing the DeskDirector for Microsoft Team App
Installing the Microsoft Teams App (Client Mode)
Installing the Microsoft Teams App (TECH Mode)
Setting up Tags for Teams Discussions (TECH Portal)
Branding the DeskDirector Teams App
DeskDirector Teams App Notifications
Contact Groups Integration with Microsoft Teams
Setting up Content Security Policy (CSP)
Advanced topic: Setting up Tech & Client Mode in the same tenancy
Integrating Microsoft Teams with DeskDirector Tech Portal
Smart Alerts for TECH Users
Integrations
Developer Resources
Getting Started
What is the Toki Iti API
API Versions & Routes
Roles & Scopes
Authorization Options
Querying the API
How to Change an Entity Through the API
API Key Authorization
OAuth Fundamentals
Understanding OAuth for Tokity Integrations: Key Concepts
OAuth Authorization Code Flow: How an App Gets Access to Tokity
OAuth App Registration
How to Register an OAuth App to Integrate with Tokity
Choosing an OAuth App Type: Confidential vs. Public Apps and Client Secrets
OAuth Personal Secrets: What They Are and When to Use Them
OAuth Administration
Configuring OAuth Settings in Tokity
Managing OAuth Authorized Sessions and User Consent
Granting OAuth Admin Consent at the Root Level
API Response Control
Uploading Attachments (Ticket API)
The Prefer Header — Overview
Controlling Returned Data (Ticket API)
Controlling Returned Data (Form Result API)
Controlling Returned Data (Workspace API)
Workspace Ordering
How Workspace Ordering Works
Creating and Reordering Workspace Groups
Adding and Reordering Tickets in a Workspace Group
Data Sync & Notifications
Delta API: Tracking Changes Over Time
Webhooks vs. Events — Differences, When to Use Which
Verifying Webhook and Event Payloads (HMAC Signature)
Ticket Widgets
Ticket Widget: Overview
How the Widget Is Requested
Ticket Widget Anatomy and Styling
Ticket Widget Actions: Leading, Secondary and Primary
Ticket Widget: Progress Type
Ticket Widget: List Type
Ticket Widget: Description Type
Ticket Widget: Form Type
Ticket Widget: Control When a Widget Refreshes
Ticket Widget: Form Results and State Across Steps
Ticket Widget: Error Responses and Debugging
Ticket Widget: Building a Multi-Step Request
Glossary
Security
Troubleshooting
Troubleshooting via Web Developer Tools
Permissions & Access - Common Issues
Contact DeskDirector Support
Troubleshooting DeskDirector Connection Issues
Desktop Portal - Common Issues
Contact Impersonation
Approvals - Common Issues
Microsoft Teams App - Common Issues
Email & Email Delivery - Common Issues
Login & Authentication - Common Issues
DeskDirector Desktop App - Installation Issues
- All Categories
- Developer Resources
- OAuth App Registration
- How to Register an OAuth App to Integrate with Tokity
How to Register an OAuth App to Integrate with Tokity

Before an application can use OAuth to access Tokity, it needs to be registered. Registration tells Tokity who the application is, where it's allowed to redirect users after consent, and how it should authenticate itself when exchanging tokens.
Platform apps vs. organization apps
Tokity has two kinds of app registrations:
- Platform applications — created and maintained by Tokity. These are available across any tenant. If Tokity ever opens registration to third-party integrators in the future, platform apps will go through a review and certification process before being published this way.
- Organization applications — created and maintained by you, the customer. These are only available within your own tenant.
As a customer, you can only create and manage organization applications. This article covers that process.
Where to register an app
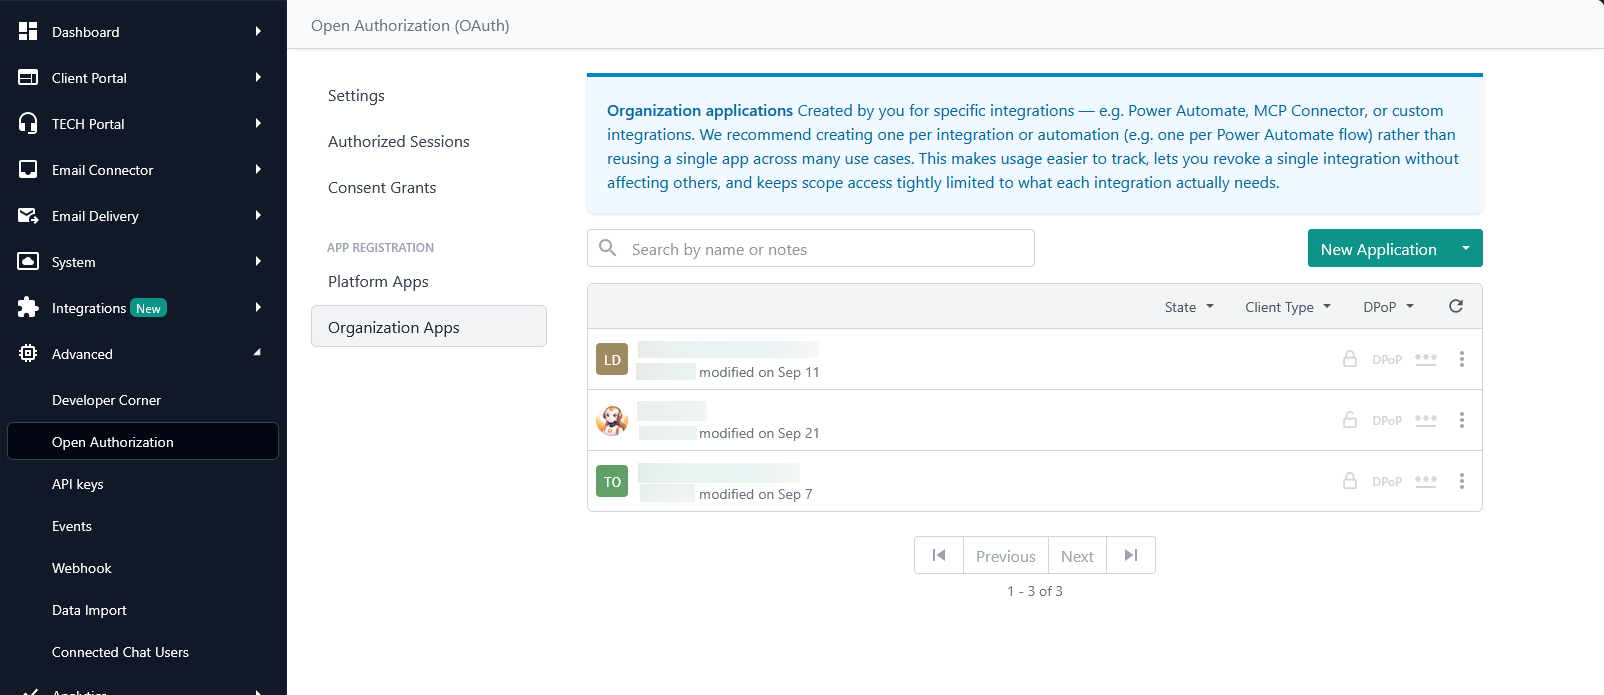
Log in to the Admin Portal.
Navigate to Advanced → Open Authorization.
Select Organization Apps.
Click New Application.
Fields you'll need to provide
Field | Description |
Name | The name of your application. |
Home Page URL | (Optional) Link to your application's home page. |
Privacy Statement URL | (Optional) Link to your application's privacy policy. |
Terms of Service URL | (Optional) Link to your application's terms of service. |
Notes | (Optional) A free-text description of the app's purpose — see below. |
Redirect URLs | One or more URLs users can be redirected back to after granting consent — see below. |
Client authentication | Whether the app is confidential or public — covered in detail in Confidential vs. Public Apps & Client Secrets. |
Demonstration of Proof-of-Possession (DPoP) | Whether DPoP is required for this app. |
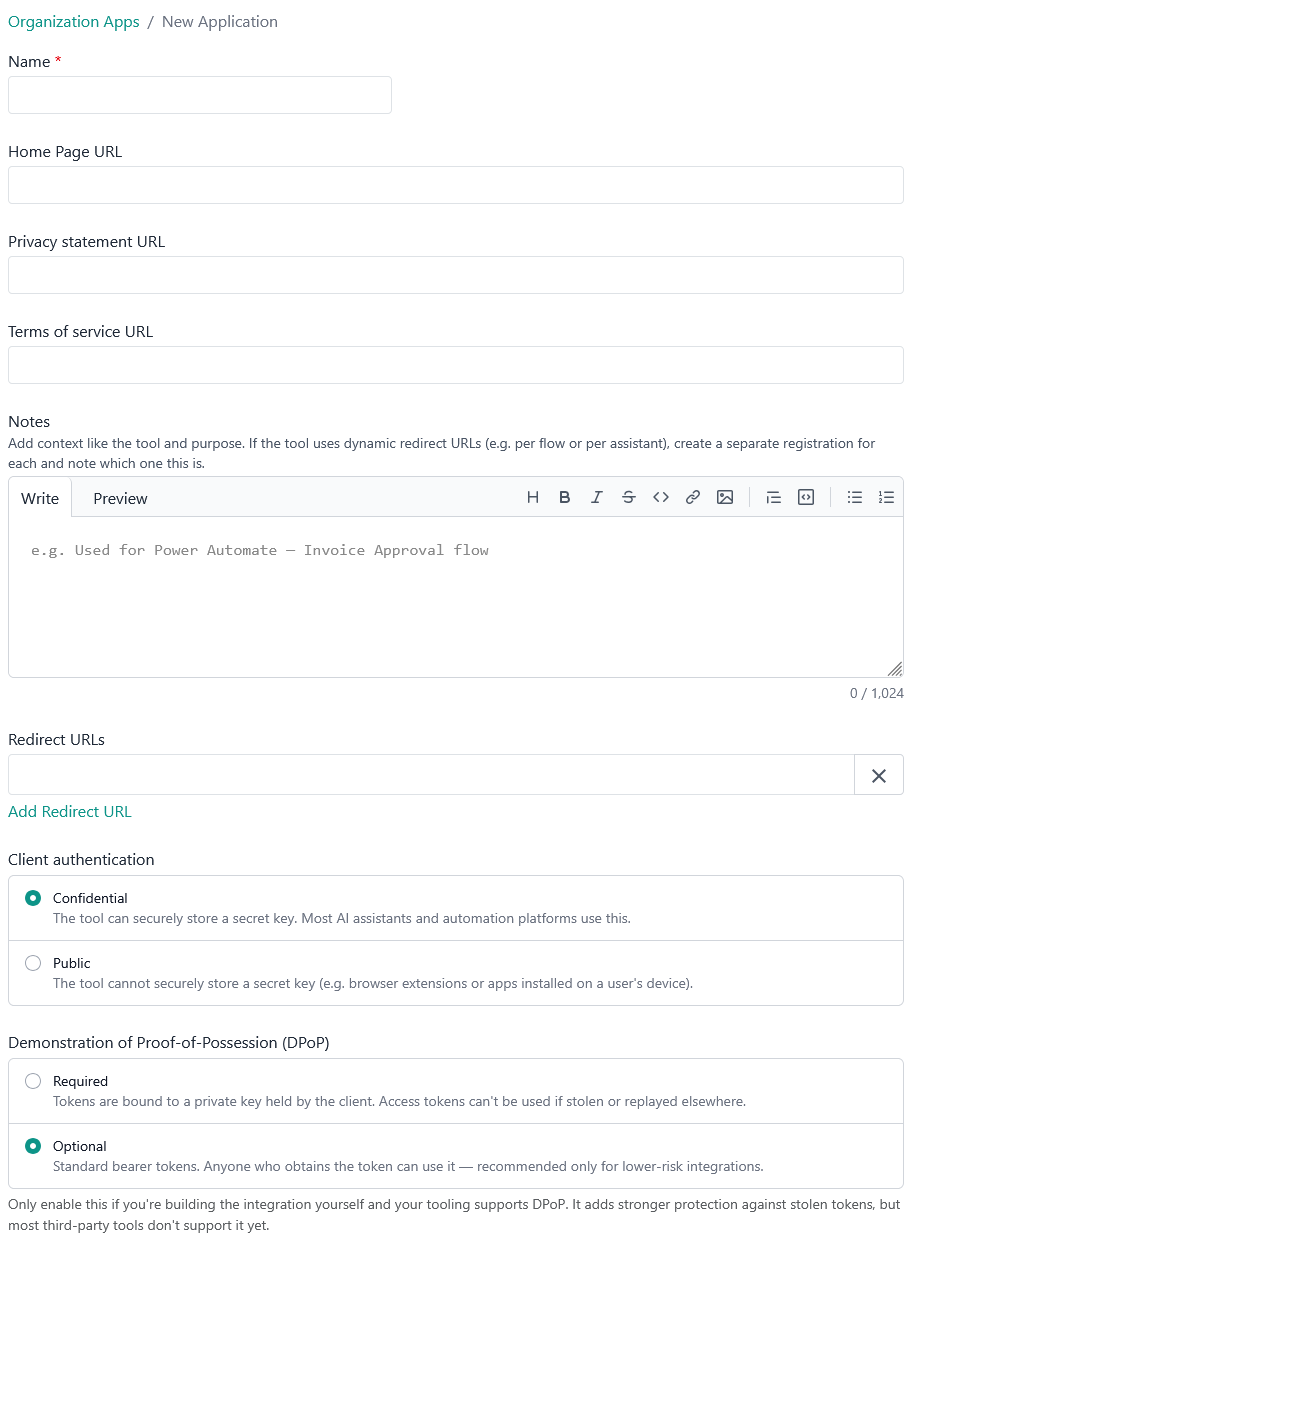
The Home Page URL, Privacy Statement URL, and Terms of Service URL are optional, and are shown to the user on the consent screen. If you're registering an app on behalf of an external application (rather than your own internal tool), use that application's actual URLs, so the person granting consent has enough context to make an informed decision.
Notes is where you describe what the app is for, and it's a good place to link to the specific thing this registration supports — for example, a particular Power Automate flow or MCP connector.
Redirect URLs
You can define multiple redirect URLs, but there are a few important restrictions:
- No wildcards, and matching is case-sensitive. Whatever you register here must match exactly what's sent in the authorization request. This is a deliberate limitation, not an oversight — allowing wildcards opens the door to redirect hijacking if a subdomain is ever taken over (for example, an old, unused subdomain being repointed to a different service). It's also a restriction called for directly in the OAuth specification itself, so this isn't a Tokity-specific choice, it's expected behavior for any compliant implementation.
- Only register a second redirect URL for diagnostic purposes — for example,
localhost, to test locally during development. In general, an app registration should have a single production redirect URL. - HTTPS only. Plain HTTP redirect URLs aren't supported. Support for application-level URLs (such as custom schemes used by mobile or desktop apps) may be added in the future, but isn't available today.
One app per integration
We recommend registering a separate application for each distinct integration — for example, one app per Power Automate flow, or one per MCP connector, rather than reusing a single app registration across several. This keeps things easy to manage: you can review, monitor, or revoke access for one integration without affecting any others. It's also part of why you generally won't need multiple redirect URLs on a single app — each integration gets its own registration, and therefore its own redirect URL, rather than sharing one app with several redirect targets.
What's next
Once your app is registered, the next decision is whether it should be a confidential or public client, and whether it needs a client secret — covered in Confidential vs. Public Apps & Client Secrets.